Deterministic state and cryptographic provenance
How hash-chained records and device signatures turn the history of a device into evidence that can be checked offline.
A device that can say what state it is in is useful. A device that can prove its state, and the path that led to it, is trustworthy. Deterministic state engines and cryptographic provenance are the two ideas that make that possible.
Determinism first
A deterministic state engine moves from one well-defined state to the next, and the same inputs always produce the same result. That sounds restrictive, and it is the point: when behaviour is fully specified, it can be reasoned about, tested exhaustively and verified.
Chaining the history
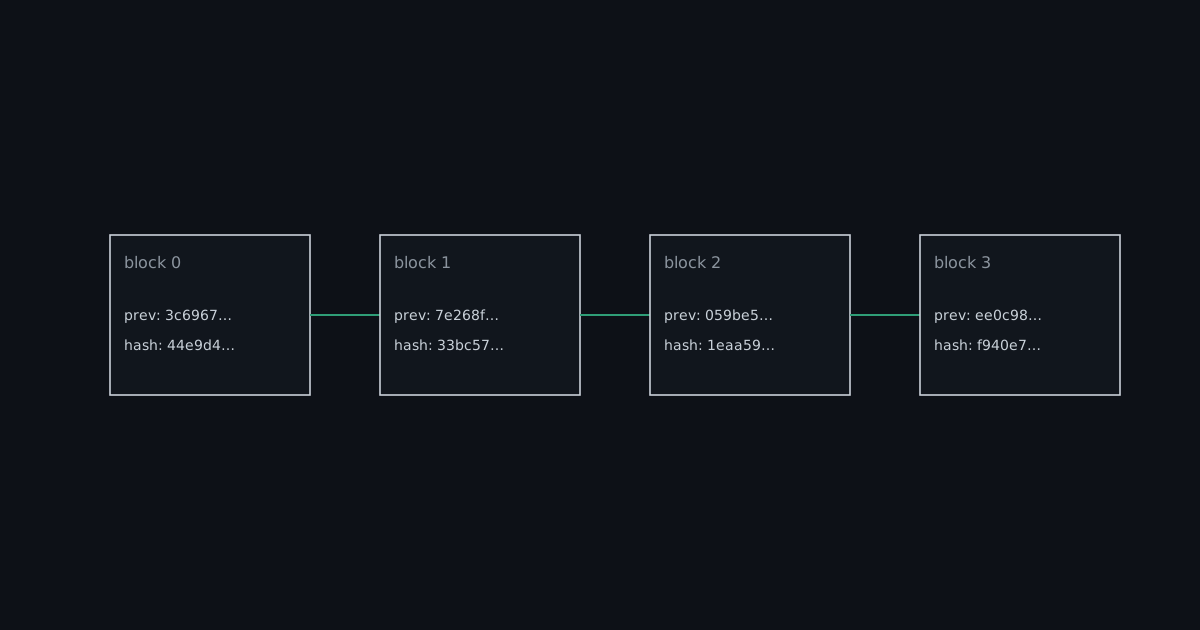
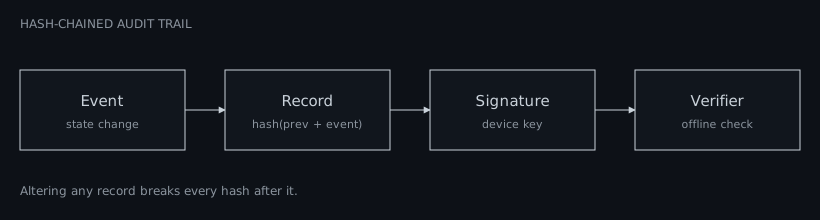
If every state change is written to a record that includes the hash of the previous record, the history becomes tamper-evident: changing any entry changes every hash that follows.
import hashlib, json

def append(chain: list[dict], event: dict) -> dict:
    prev = chain[-1]["hash"] if chain else "0" * 64
    body = json.dumps({"prev": prev, "event": event}, sort_keys=True).encode()
    record = {"prev": prev, "event": event, "hash": hashlib.sha256(body).hexdigest()}
    chain.append(record)
    return record

def verify(chain: list[dict]) -> bool:
    prev = "0" * 64
    for r in chain:
        body = json.dumps({"prev": prev, "event": r["event"]}, sort_keys=True).encode()
        if r["prev"] != prev or r["hash"] != hashlib.sha256(body).hexdigest():
            return False
        prev = r["hash"]
    return True
This sketch shows the principle only. A real system also signs records with a key that never leaves protected hardware, so a verifier can check both integrity and origin.
From a log to evidence
| Ingredient | What it gives you |
|---|---|
| Deterministic state | Behaviour that can be specified and tested |
| Hash chain | Tamper-evident history |
| Device signature | Proof of origin |
| Offline verifier | Checking without a trusted intermediary |